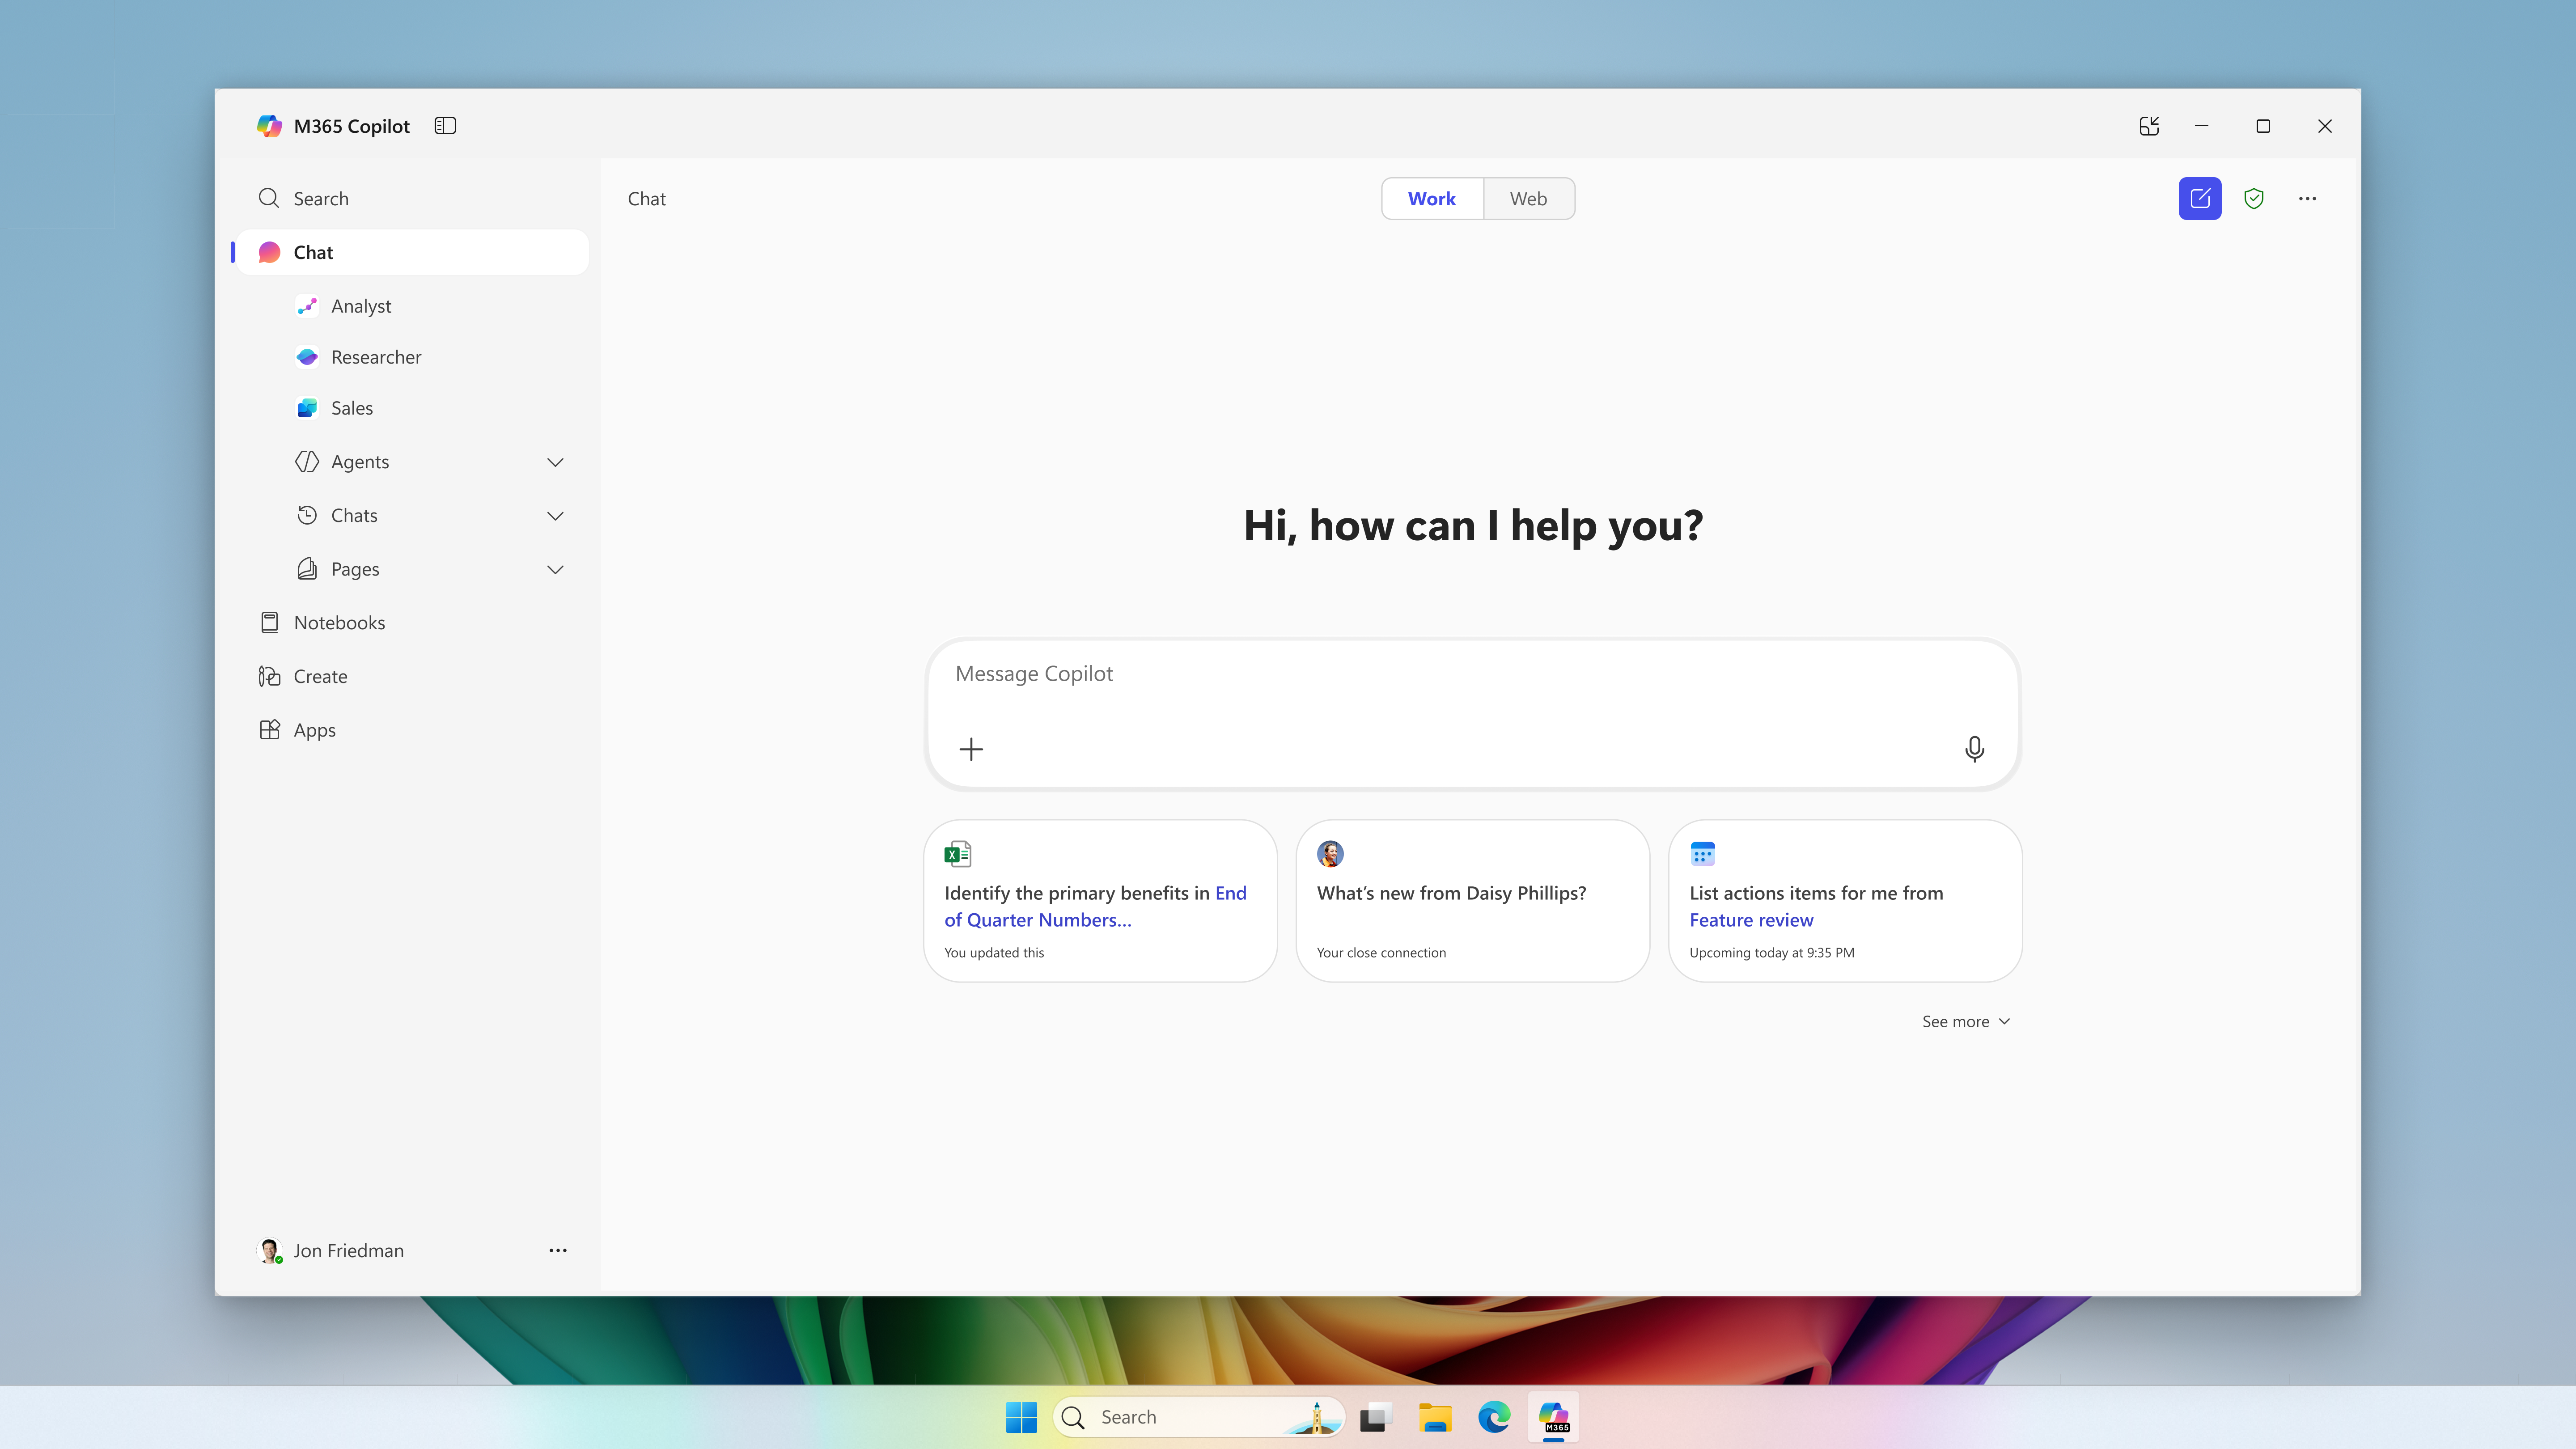
Microsoft extends usage limits to additional Copilot Chat features for users without a Microsoft 365 Copilot license in commercial organizations. The notifications call for support preparation and a review of license requests, without turning every limit into a recommendation to buy.
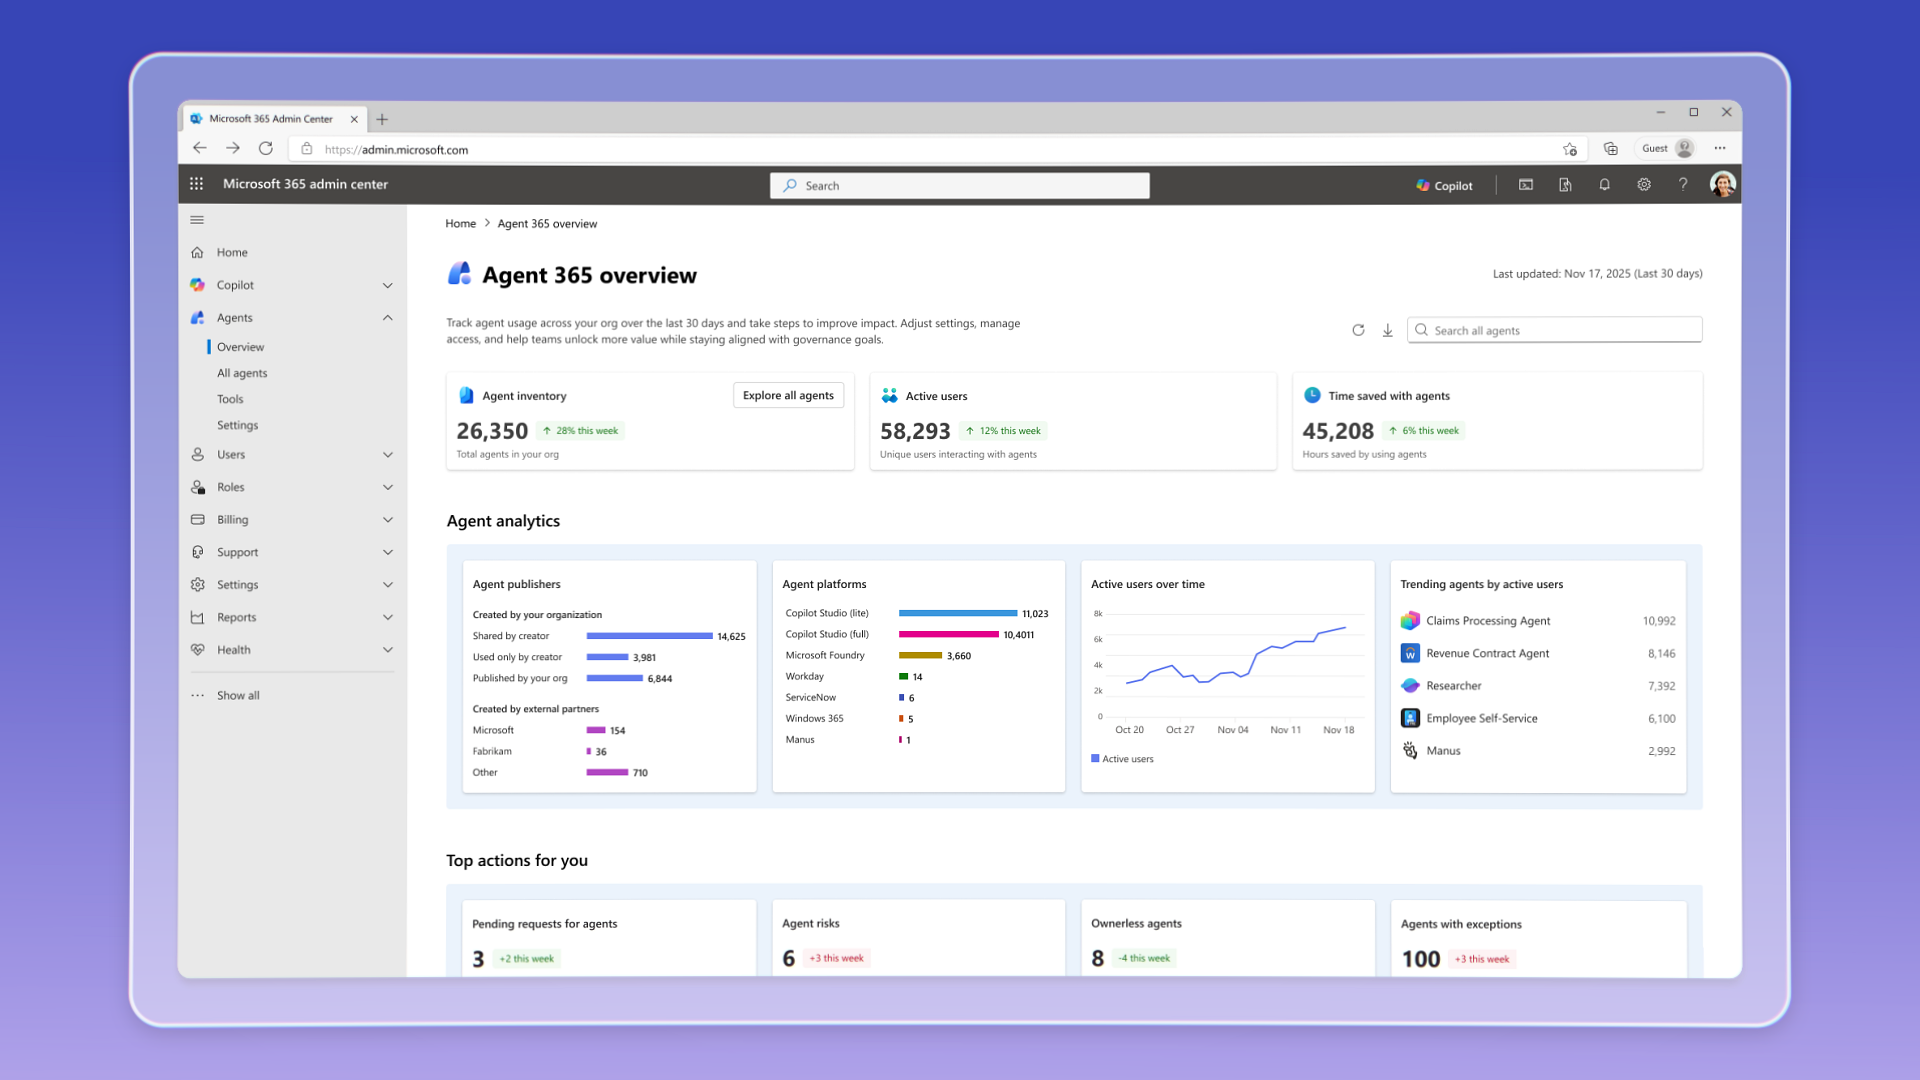
Agent 365 has been generally available commercially since May 1, 2026, with per-user licensing; the sources consulted do not specify Action Center’s rollout status.
Two settings merged into the Business Central code control quantity restoration on sales and purchase orders. Both remain enabled by default; the 30.0 milestone does not establish availability in a tenant.
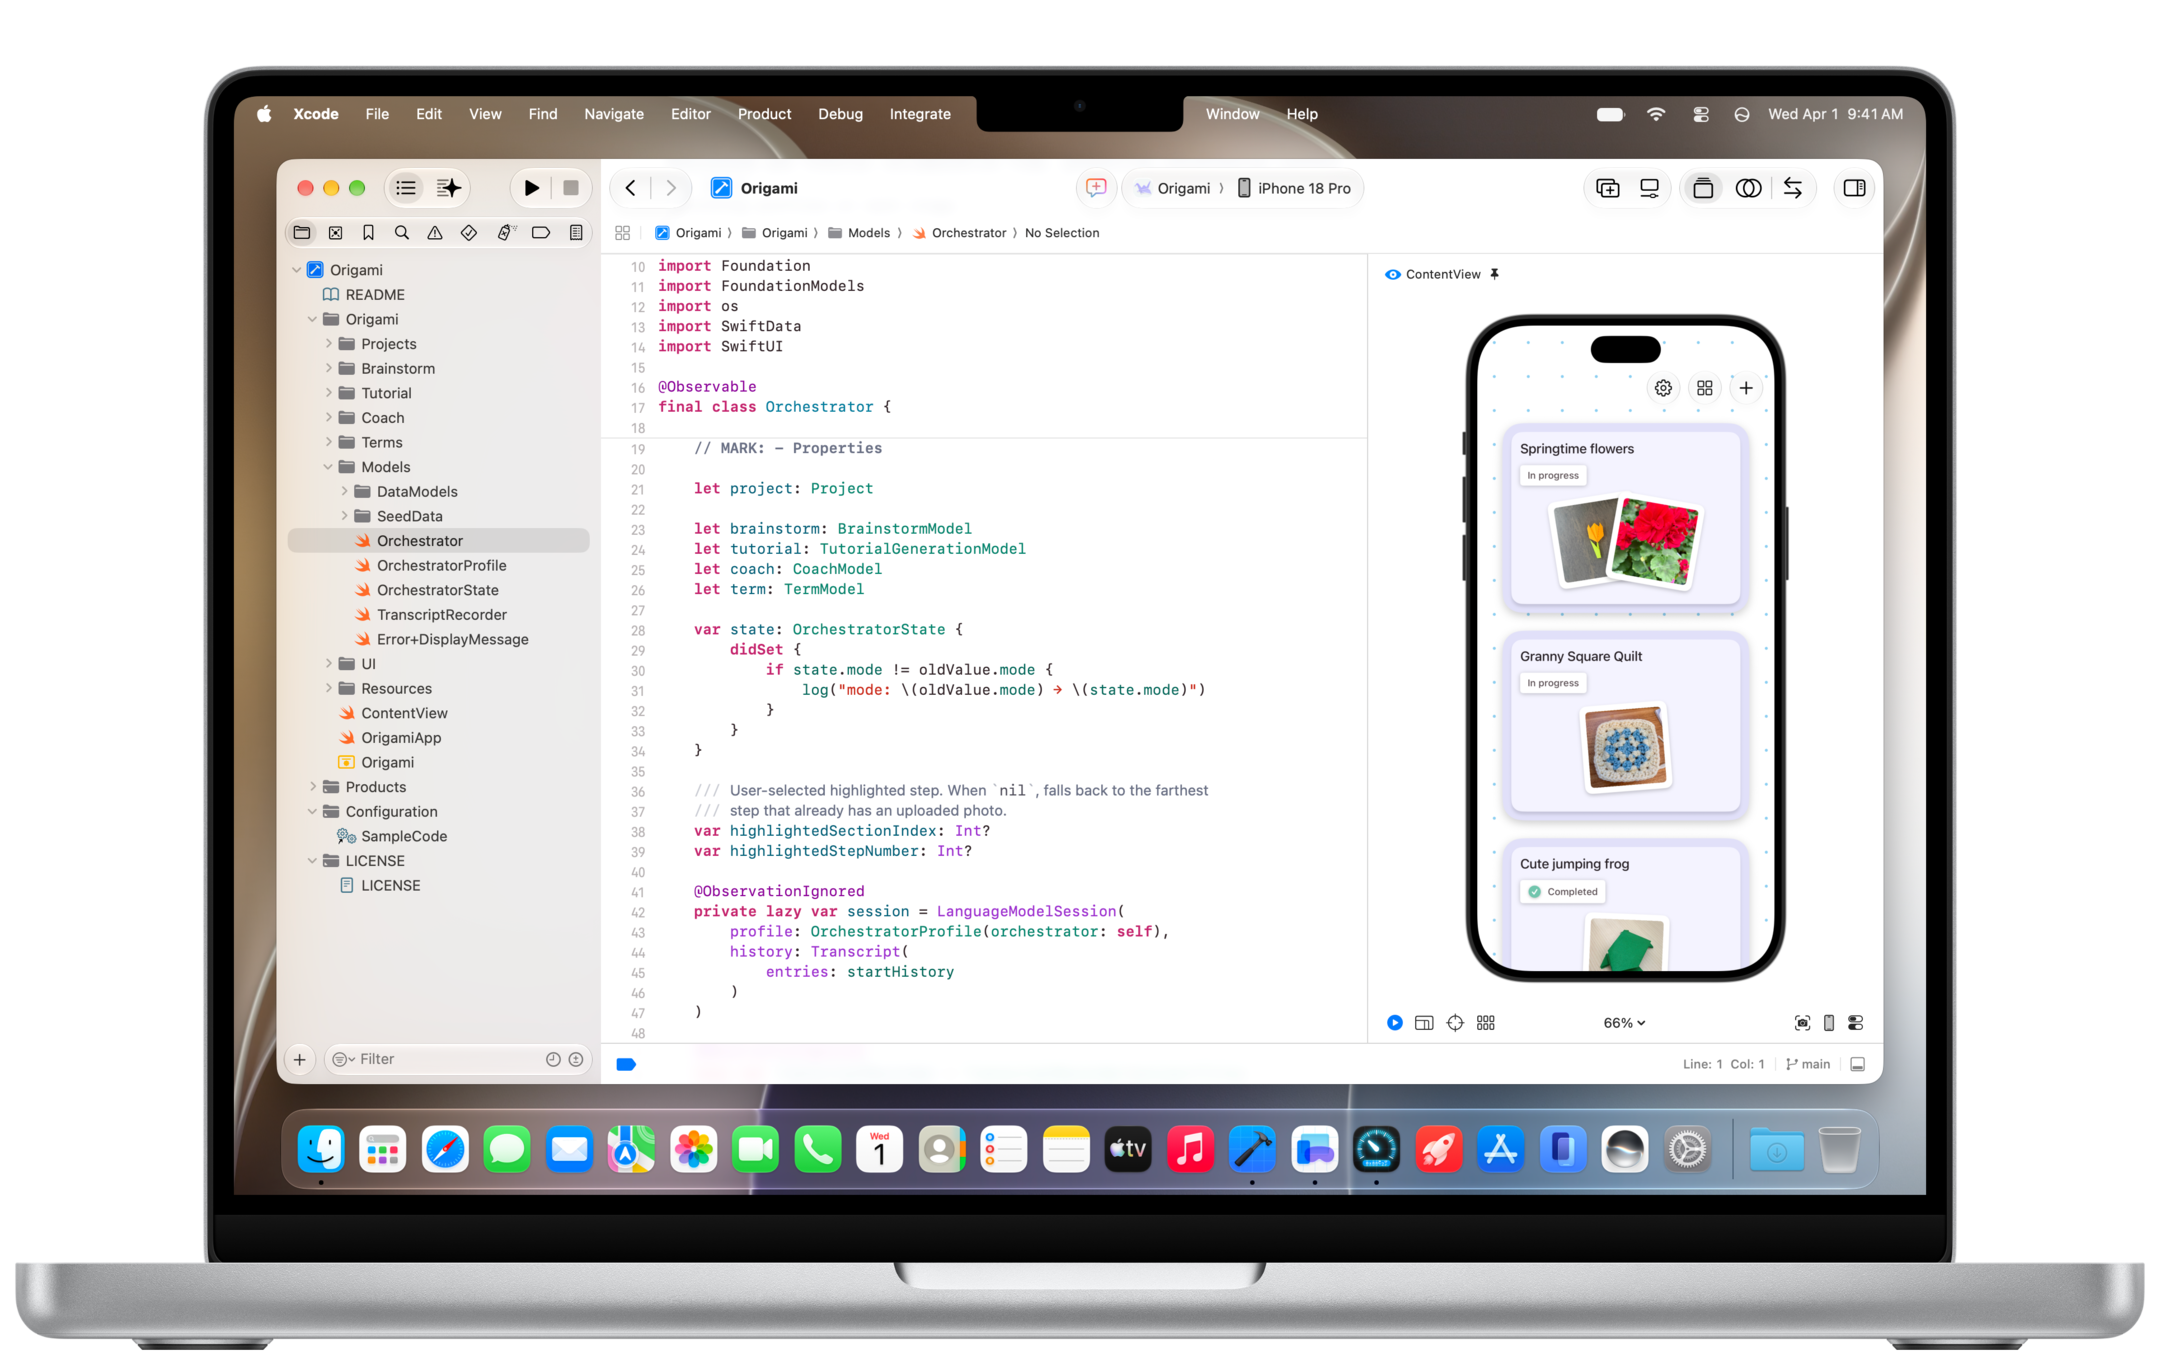
Copilot comes to Xcode's built-in coding assistant in public preview and to JetBrains Air. Agent Merge also improves pull request tracking, with different conditions depending on the environment.
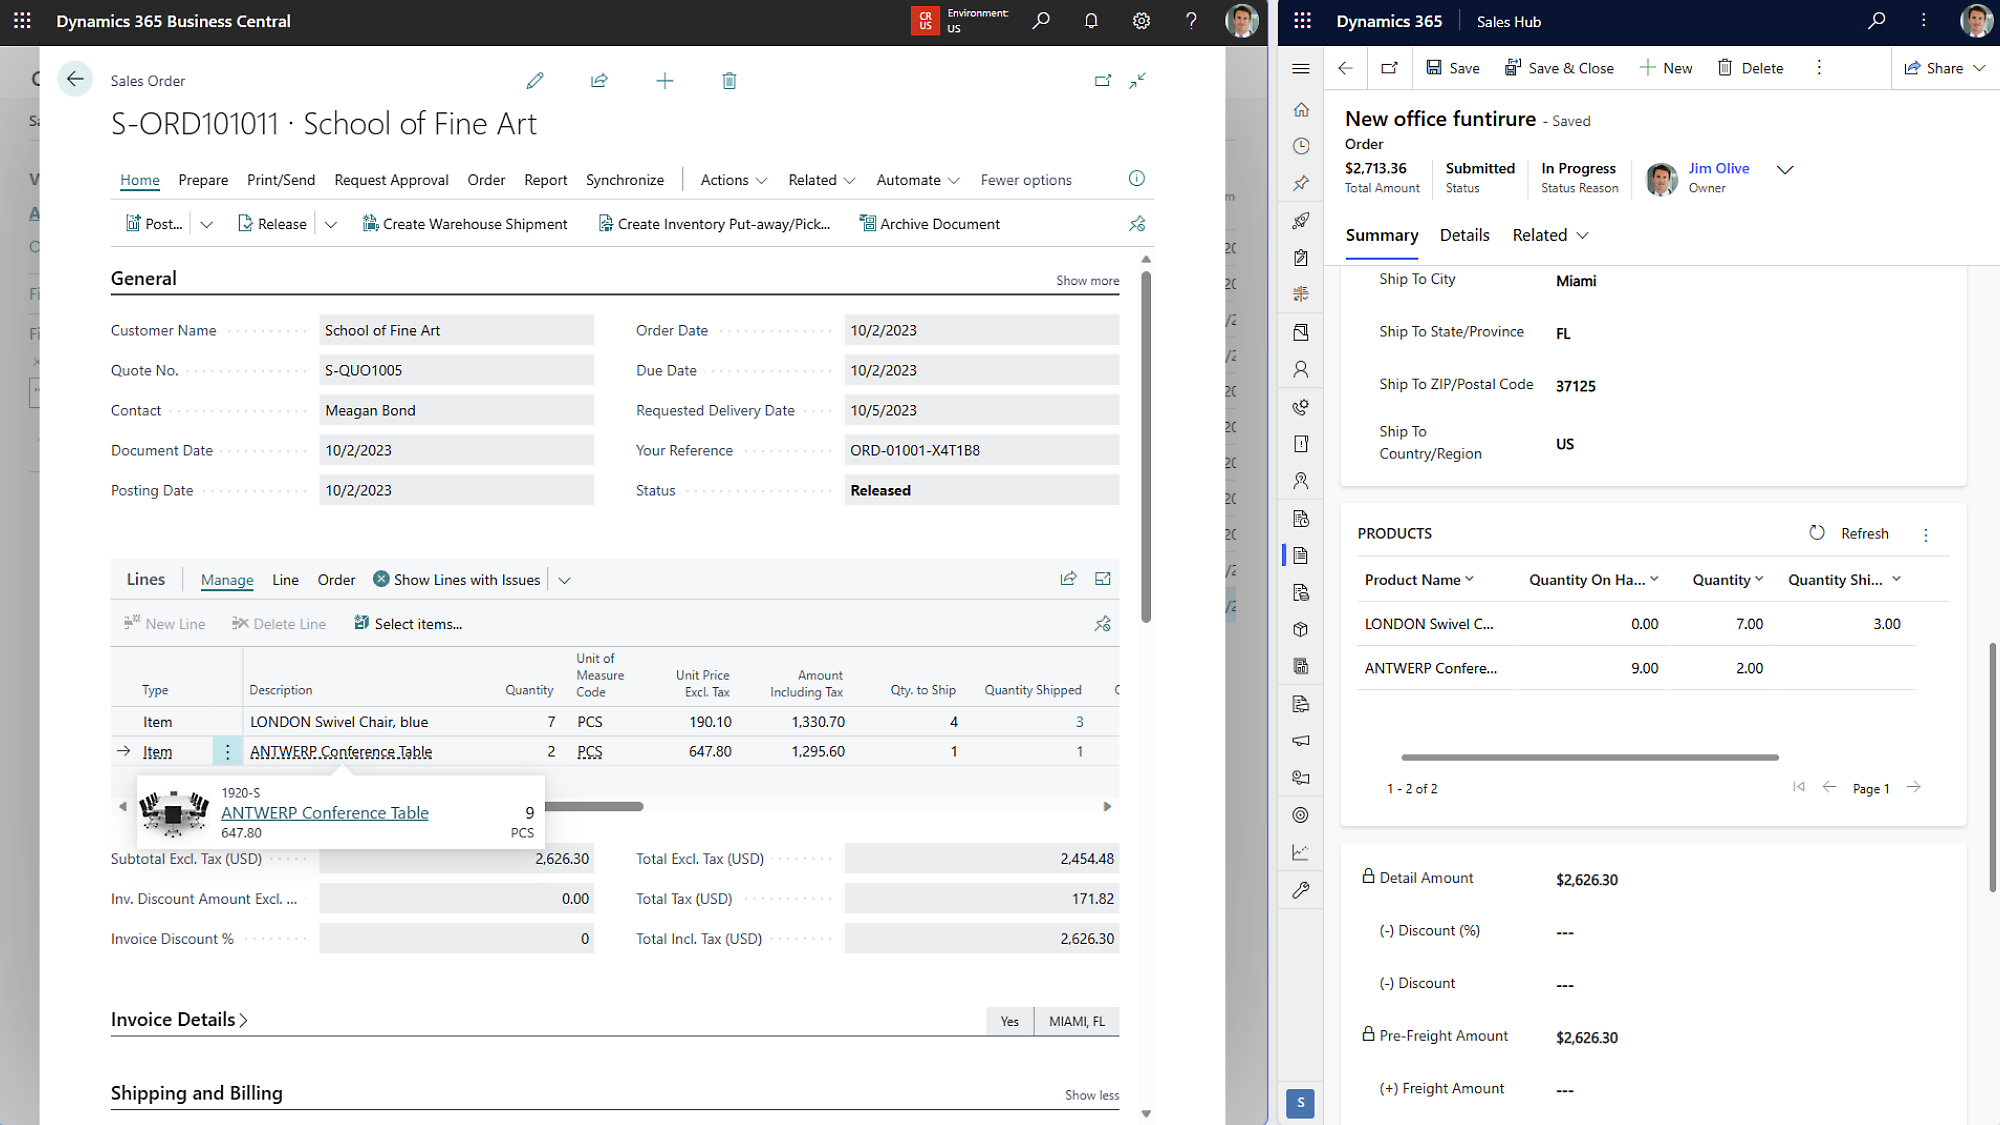
A BCApps commit describes a numbering conflict when importing Dynamics 365 Sales orders into Business Central with automatic recurring lines, relevant to acceptance testing for the sales integration.
Restrictions involving macOS 27 and Xcode 27 require a review of code extraction. Analysis without a build offers alternatives with limits that depend on the language.
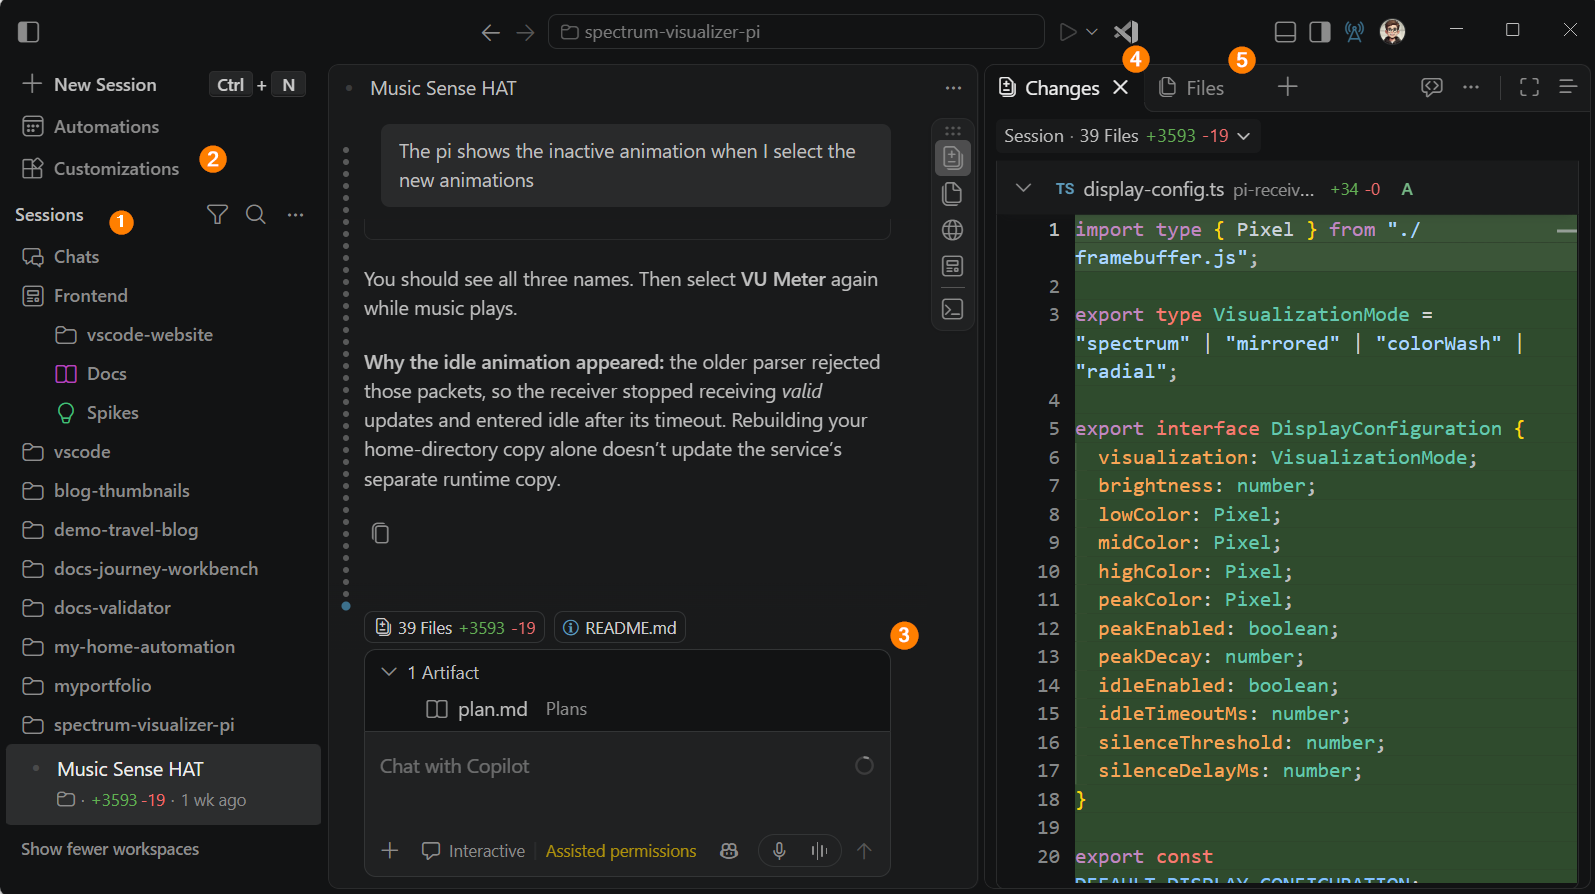
The impact dashboard adds Copilot Chat and the VS Code Agents window. The broader coverage reveals more usage patterns, but requires distinguishing feature engagement, adoption phases, and comparable reporting periods.
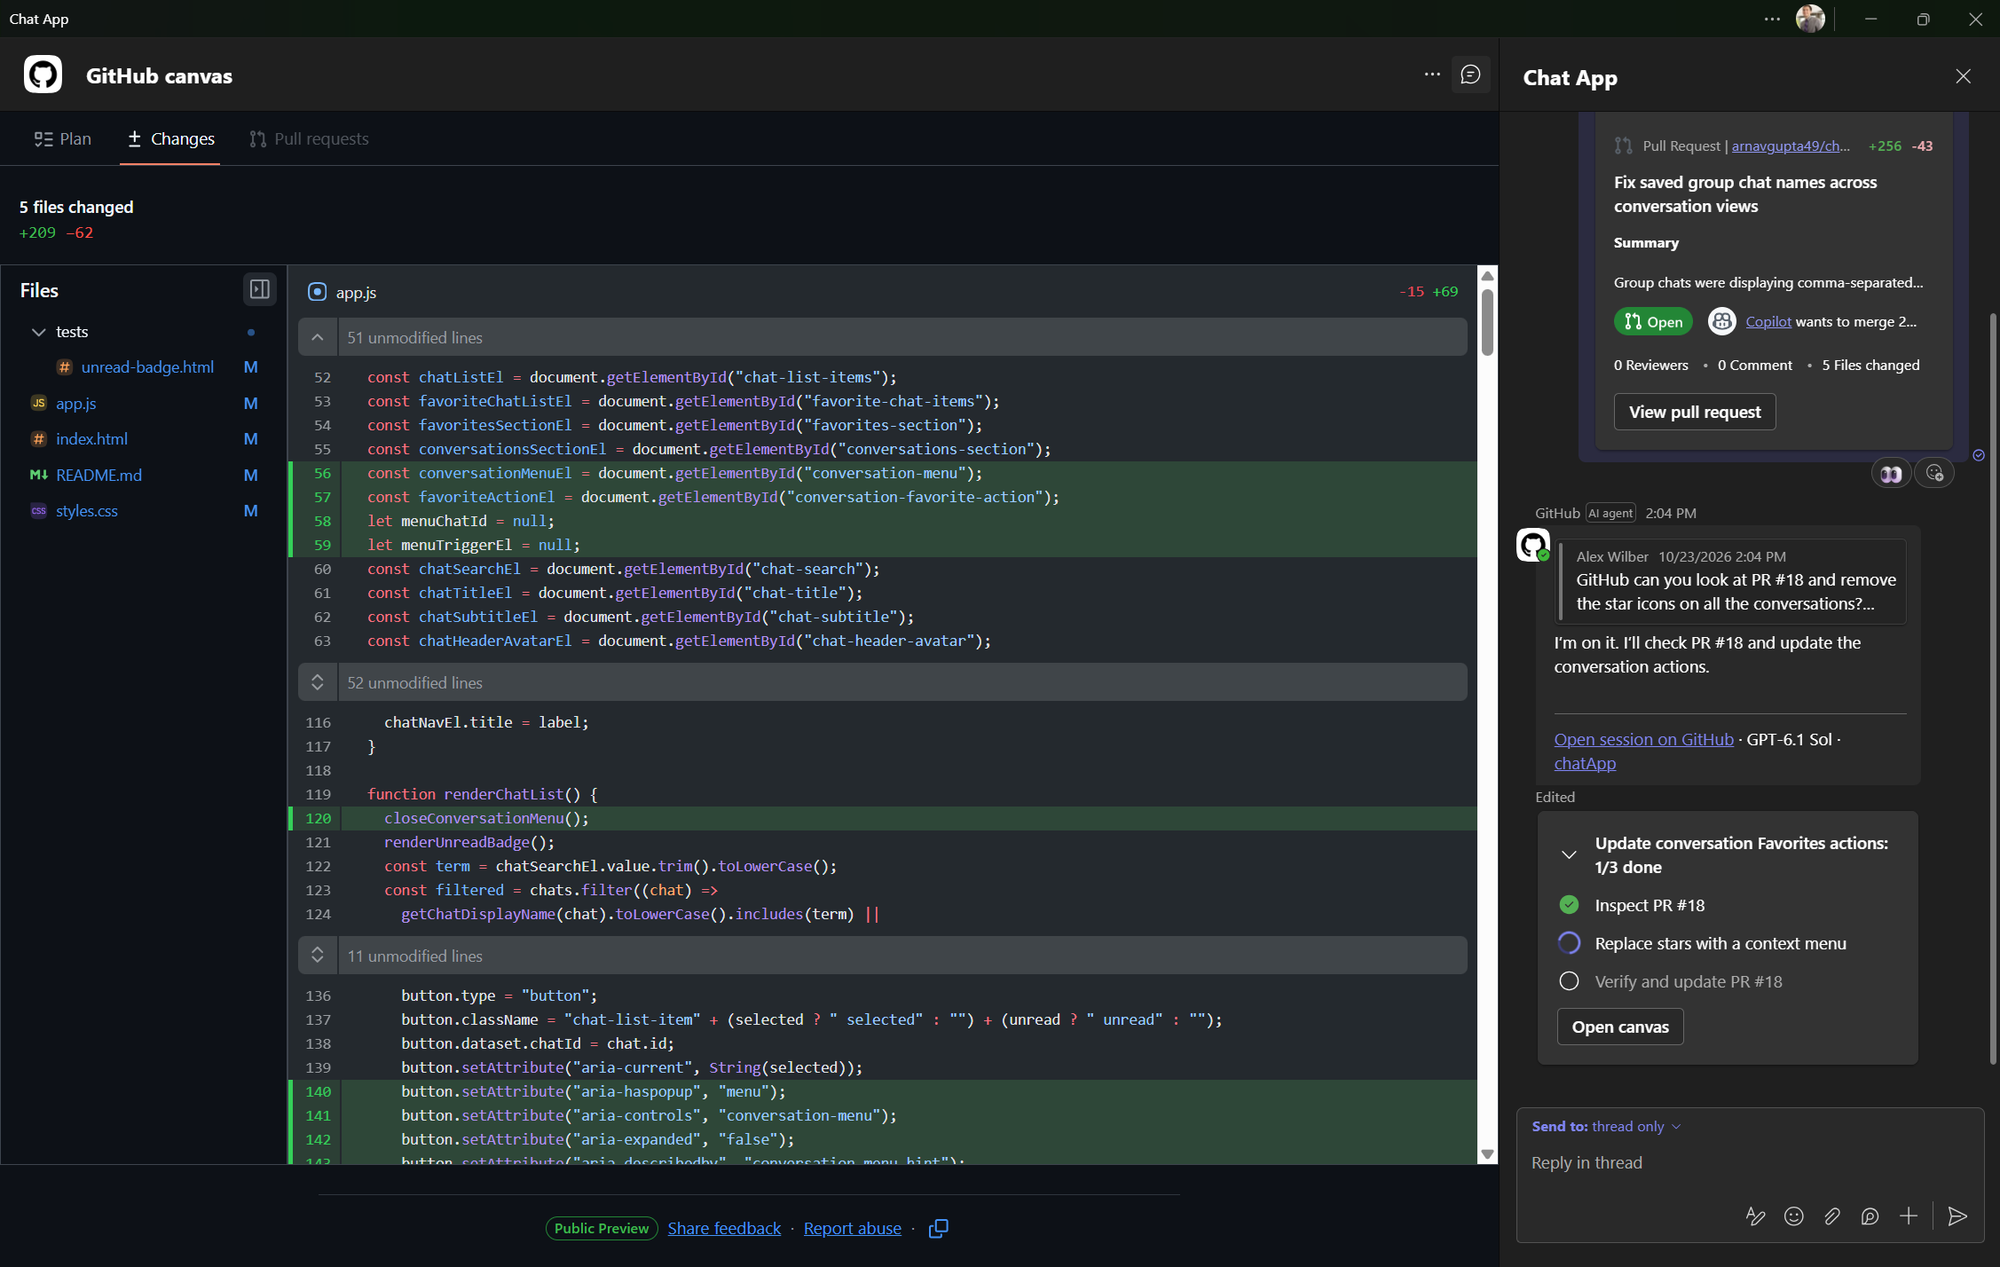
Canvas lets teams follow the plan and review changes alongside their Teams conversation. Access requires a paid Copilot plan and remains subject to permissions, policies and usage.
GitHub · Announcement: · Editorial review
Canvas alongside the Teams conversation. Screenshot: GitHub.
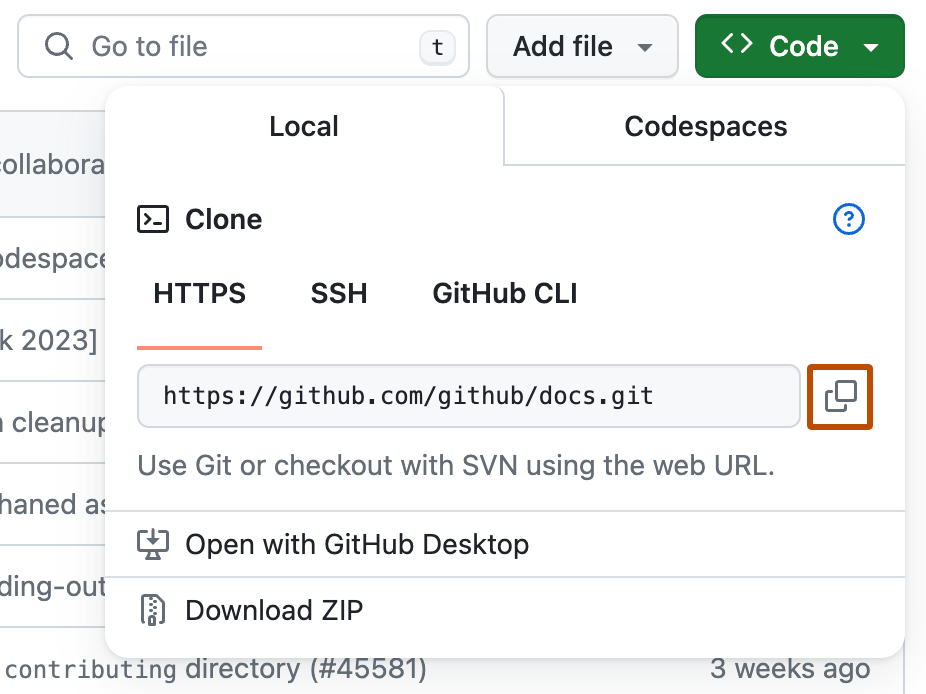
The October 19, 2026 announcement describes temporary protection against unusual traffic: some public HTTPS clones and fetches may fail requesting authentication. It covers all github.com plans and can affect legitimate traffic; it is not a blanket requirement. Authenticated HTTPS operations, SSH, pushes, and unrelated web/API traffic are unaffected. Users can authenticate and retry, or wait until protection is lifted.
Choosing credentials for each environment
GitHub’s authentication documentation distinguishes browser access from Git client authentication. An account password cannot authenticate Git over HTTPS. GitHub CLI and Git Credential Manager provide ways to manage that access.
The table brings together GitHub’s stated options and the requirements to check before changing an automation.
Environment
Credential
Limit to check
GitHub Actions
The built-in GITHUB_TOKEN, used by actions/checkout by default.
actions/checkout recommends contents: read. The token is scoped to the workflow repository; another private repository requires a credential with access.
The App needs the Contents permission and repository access. The installation token expires after one hour, so automation must account for renewal.
Manual work over HTTPS
GitHub CLI, Git Credential Manager, or a personal access token (PAT).
Check which account and credential the client performing the operation uses.
What to review in automation
Nexo’s interpretation: identify where each step depends on anonymous access. Mapping that path helps teams decide where to configure authentication and where to accept a delay, without attributing every download error to the same cause.
Locate each git clone and git fetch, including operations that might run inside containers or helper scripts. These are examples of places to review, not observed incidents.
Check the protocol, repository, and credential mechanism in the environment performing each access. The remote repository guide explains that git remote -v shows configured addresses; this alone does not confirm authentication.
Retain the error message without exposing secrets. To diagnose other failures, the cloning guide suggests checking HTTPS connectivity, repository permissions, and whether the branch exists.
Synthetic example: a download inside a container
Suppose a workflow retrieves its repository through actions/checkout and then starts a container that clones a public dependency without credentials. Review the two accesses separately: authentication in the first step does not establish how the container process authenticates.
In this fictional case, the team would check the target repository, how to provide a read credential with access, and whether the download can be deferred through limited retries with pauses. This is a proposed review, not a universal configuration. The example has not been executed and does not represent a real incident.
Created with AI assistance and reviewed by Nexo Community. Practical proposals and editorial interpretation are distinguished from documented facts.